Capture remains with your provider
The payment surface uses the SDK and certification path your institution has already assessed.
Commerce
Intelligence
Infrastructure
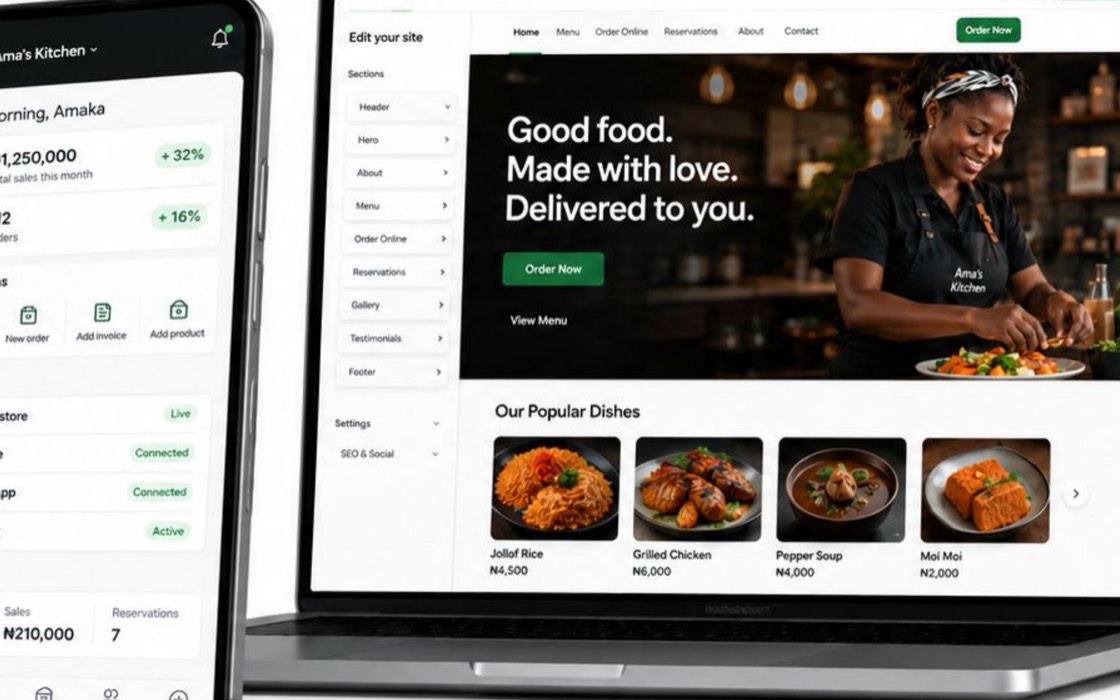 Why institutions choose Box
Keep the brand, records, rails, and merchant relationship.
Start here
By merchant activity
By deployment
 See it running
OlivePay licensed Box. The tills are already in the field.
Payment capture is delegated to the assessed SDK your institution supplies. No card number, PIN, CVV, or cryptogram crosses a Box library boundary.
A smaller boundary
Box records the order, the provider reference, and the result needed to operate the sale. The sensitive payment credential remains with the payment implementation already governed by your institution.
The payment surface uses the SDK and certification path your institution has already assessed.
Payments bind through a port. Box modules resolve an implementation without reading its secrets.
Orders, refunds, voids, staff actions, and provider references remain connected for review.
Follow one payment
Move through the transaction to see which system handles each part and what Box retains.
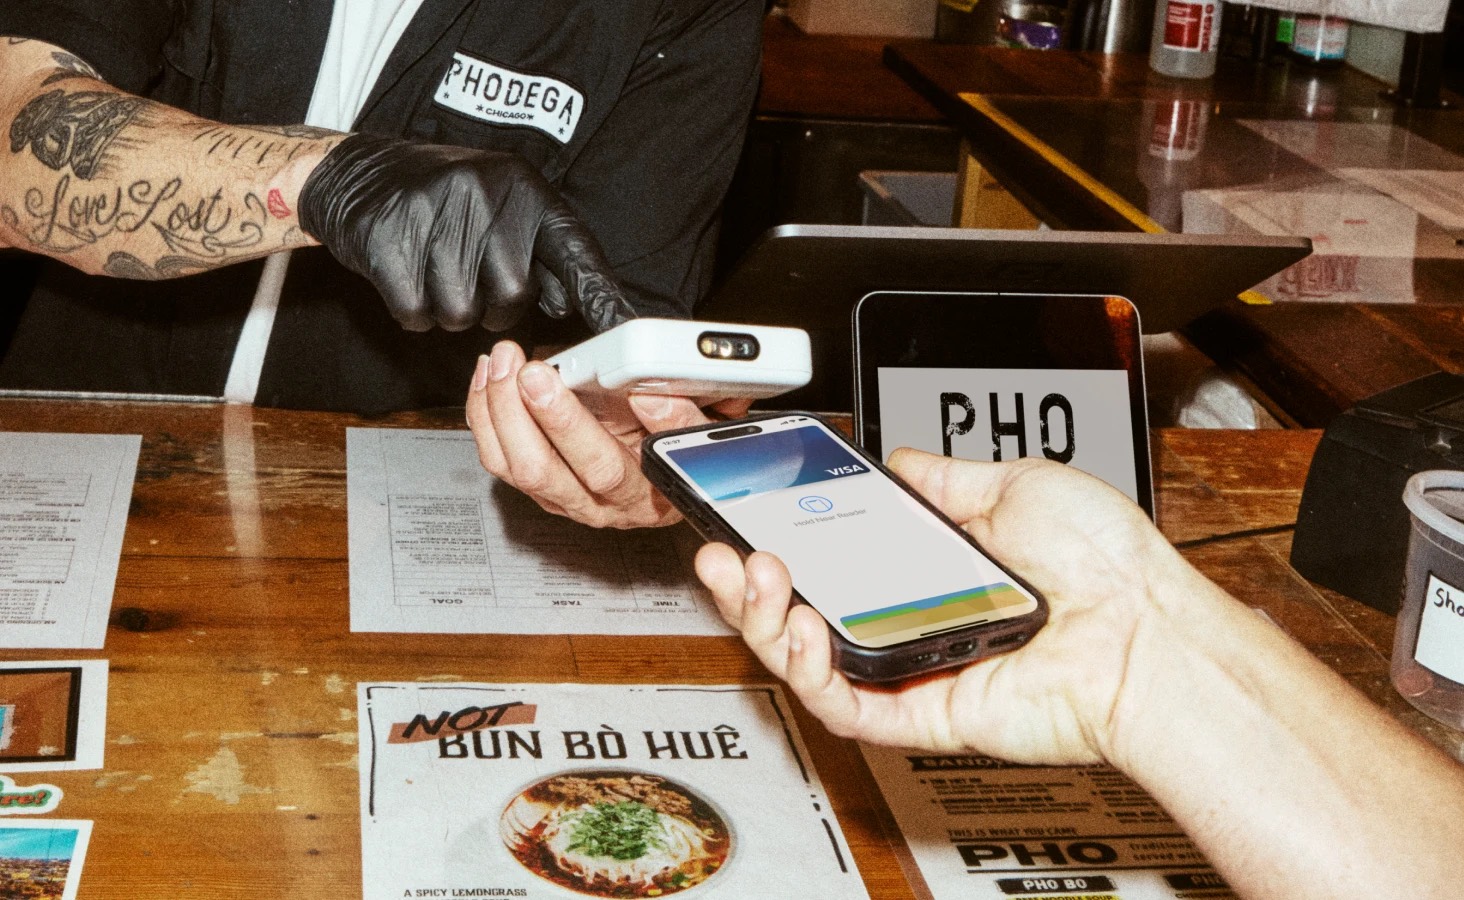
Your assessed SDK
The customer presents a card or wallet directly to the payment implementation selected by the institution.
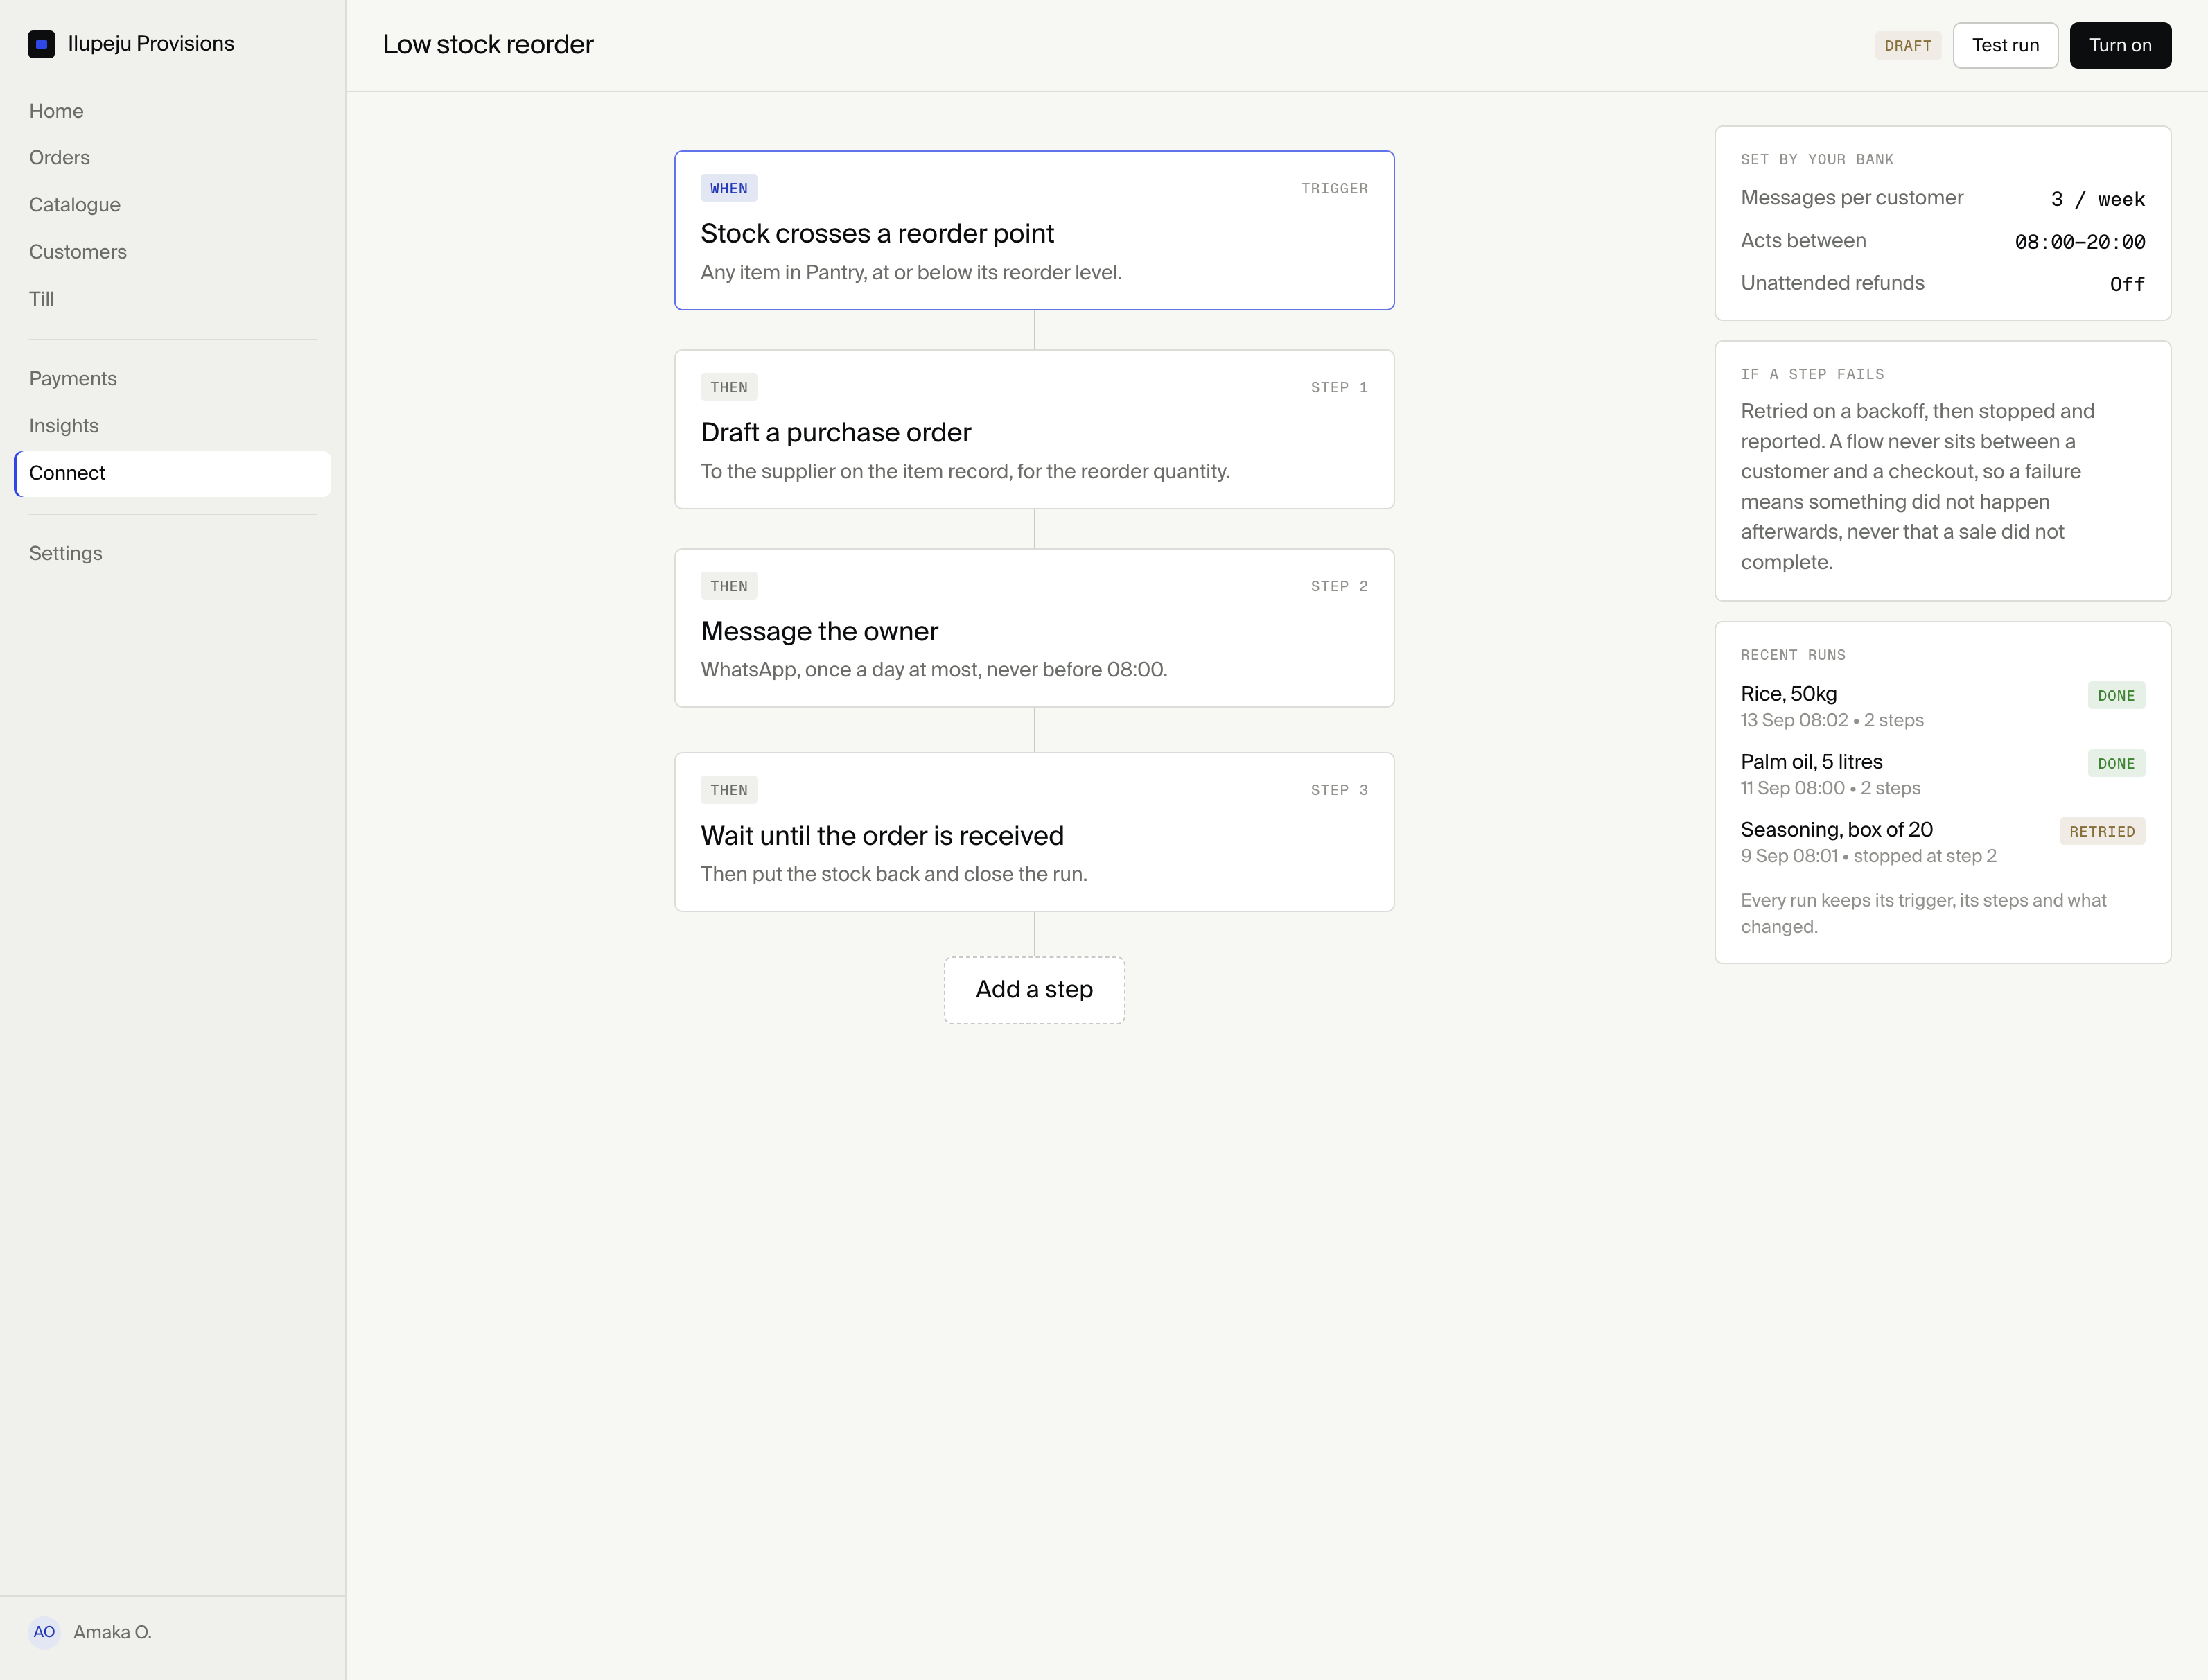
Your payment adapter
The payment port binds to an adapter the institution supplies. Provider credentials remain inside that implementation.
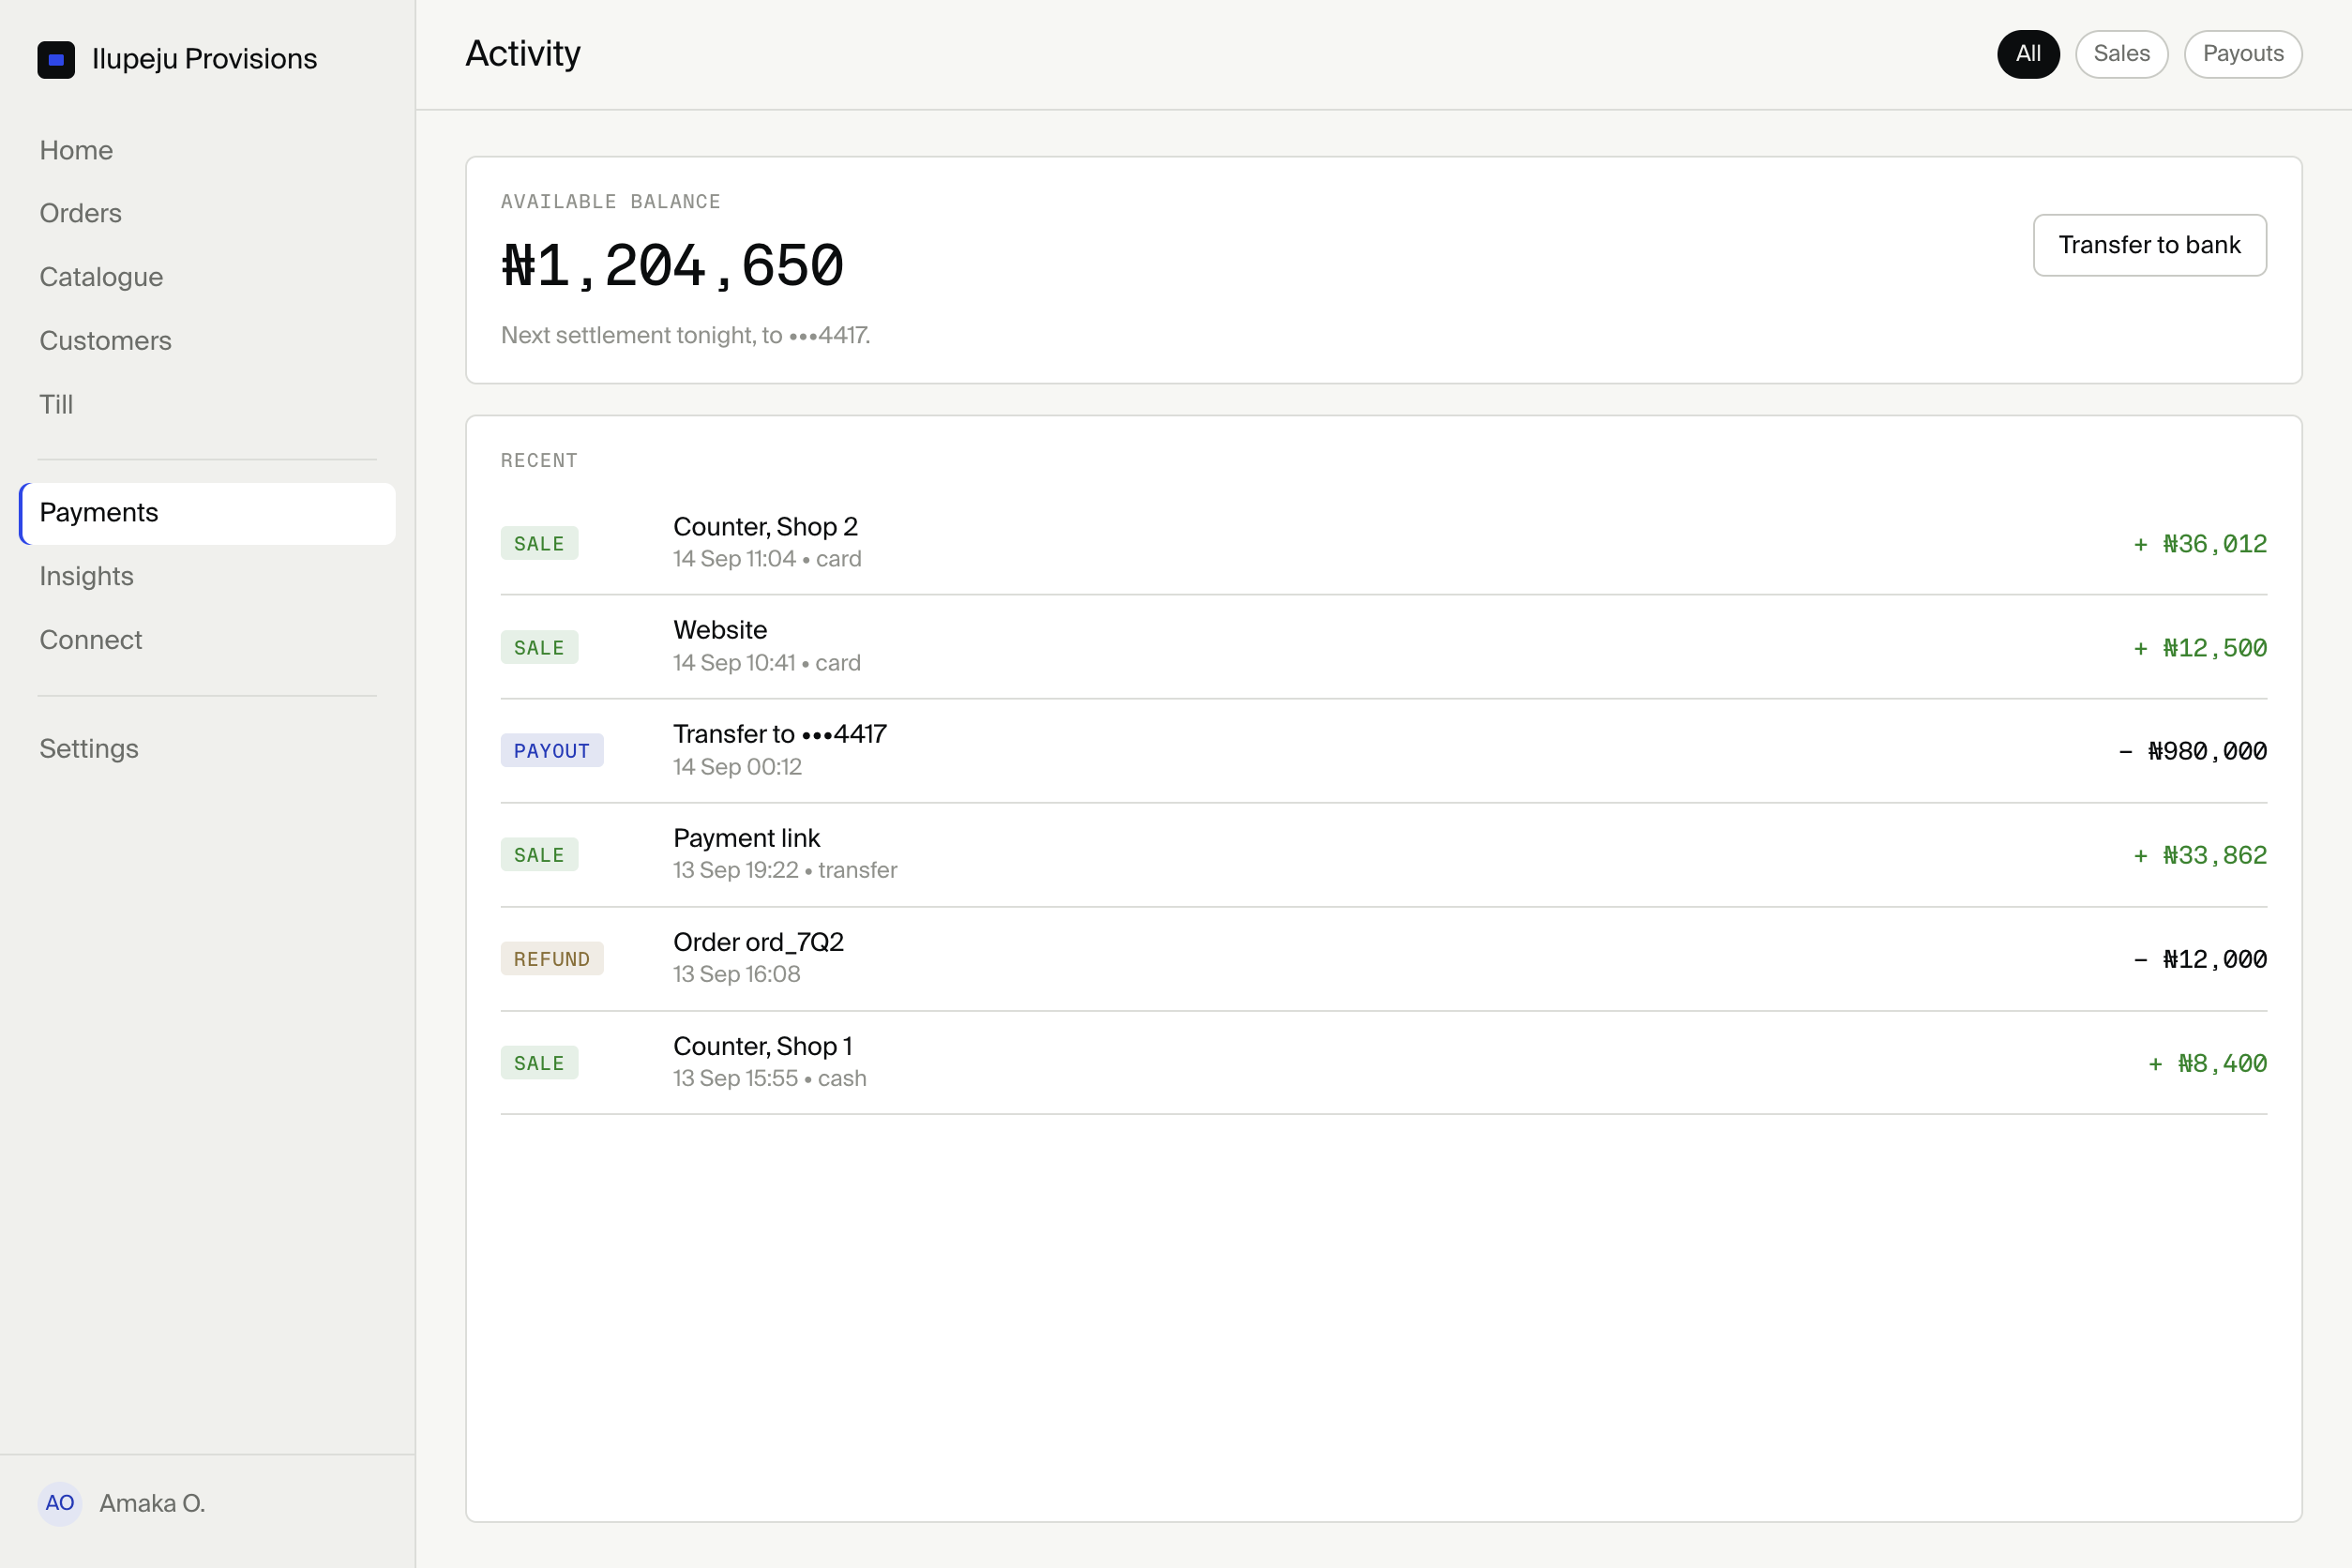
Your commerce record
The order stores the provider reference and payment state needed for refunds, reconciliation, and support.
Beyond capture
01
Tills enrol with a platform integrity token and hardware backed keys, so a device in the field is one the institution put there.
02
Merchants give each person the routes their work requires. Refunds, voids, and edits remain tied to the person who performed them.
03
The payment stays attached to its order, channel, staff action, and provider reference instead of becoming an isolated total.
04
Nothing changes on a running deployment until its operator runs the upgrade, making review possible before a release is live.
Shared responsibility
Your institution operates
They run inside the network, region, monitoring, retention, and identity controls your institution already governs.
Box operates centrally
These systems do not hold merchant records. The render resolves a host and fetches from the correct deployment for that request.
For security reviewers
We provide component boundaries, package provenance, deployment responsibilities, and the decisions worth reviewing before a pilot. We do not claim certifications that cannot be attached to a report.
No. Payment capture is delegated to the institution supplied SDK. No card number, PIN, CVV, or cryptogram crosses the Box library boundary.
Inside the payment implementation the institution supplies. The Box shell binds to that implementation through a port and does not read its gateway credentials.
No certification claim is made here. The transaction is governed by the assessed payment SDK and operating environment selected by the institution.
Yes. Payment capabilities depend on a contract rather than one provider. A new adapter can replace the implementation without changing the order model.
Review Box
Bring your security, payments, and platform teams into the first conversation.
Contact sales